Secure Messenger
An engineering prototype of a secure messenger core, with no interface. It proves the essentials: a message can’t be read by others, can’t be altered unnoticed and can’t be delivered twice.
How it works
Each profile has a password and a key pair. Contacts are exchanged as files with a key fingerprint to compare. A message is signed with Ed25519 and encrypted with post-quantum ML-KEM-768 together with ChaCha20-Poly1305. History is kept in SQLite, and the text never sits on disk in the clear.
What it rejects
A replay of a message already received, a message with one flipped bit, a wrong password and an impostor who took the same name with a different key. All of it is shown in the real runs below.
Honest about the limits
This is a prototype: it has no network transport, no forward secrecy and no external audit. It shows how we build a cryptographic core and prove it with tests.
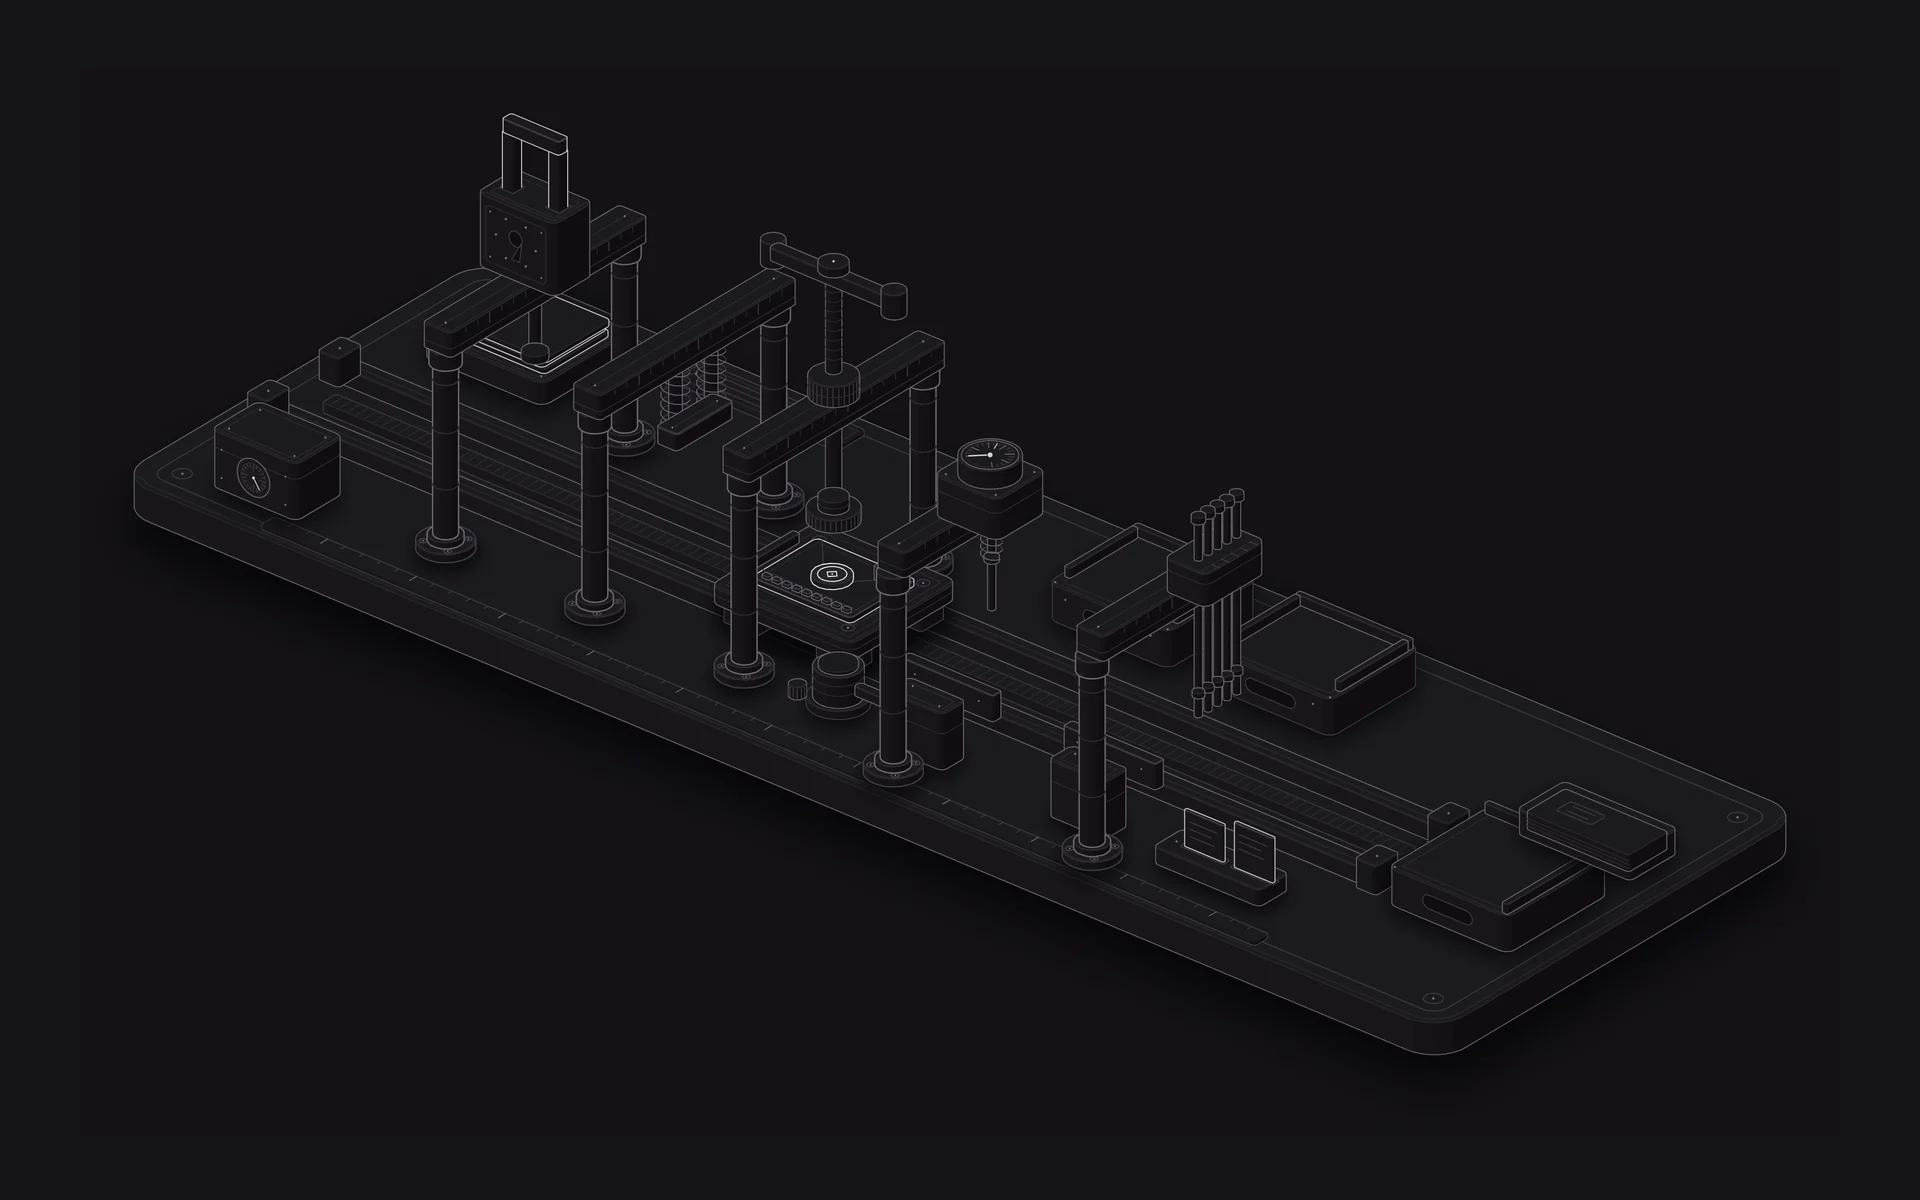
A sealing press for letters
A letter passes the key lock, the envelope sealer and the wax signature stamp. On the receiving side, a feeler at the gate checks the seal and rejects a letter with one broken bit, and a counter stops a replay.
Screens
Under the hood
- C++20, CMake, OpenSSL and SQLite, strict compiler flags and a sanitizer build.
- Ed25519 for signatures; ML-KEM-768, HKDF and ChaCha20-Poly1305 for encryption.
- The profile password is hardened with scrypt.
- About 1,500 lines of code; the program is about 120 KB.
- Builds for Linux, macOS and Windows.
C++20 · OpenSSL · SQLite · CMake